Blog · EU AI Act status reviewed 2 September 2026 · 7 min read
EU AI Act Nudification Ban: What AI Deployers Should Check
A practical deployer review guide for the Regulation (EU) 2026/1744 provisions covering non-consensual intimate-content generation and AI-created child sexual abuse material.
Reviewed: 2 September 2026.
Current-law source basis: Regulation (EU) 2026/1744 and Regulation (EU) 2024/1689 as consolidated from 27 July 2026. The Commission announcement and Council releases of 7 May 2026 and 29 June 2026 provide legislative history; the Commission AI Act FAQ is an institutional explanation. This page is educational and does not provide legal advice or compliance guarantees.
Quick answer: Regulation (EU) 2026/1744 adds new Article 5 provisions for AI practices involving realistic non-consensual intimate or sexually explicit material and child sexual abuse material. That matters now for vendor screening, internal use-case reviews, content-safety controls and evidence files, while Regulation (EU) 2026/1744 entered into force on 27 July 2026.
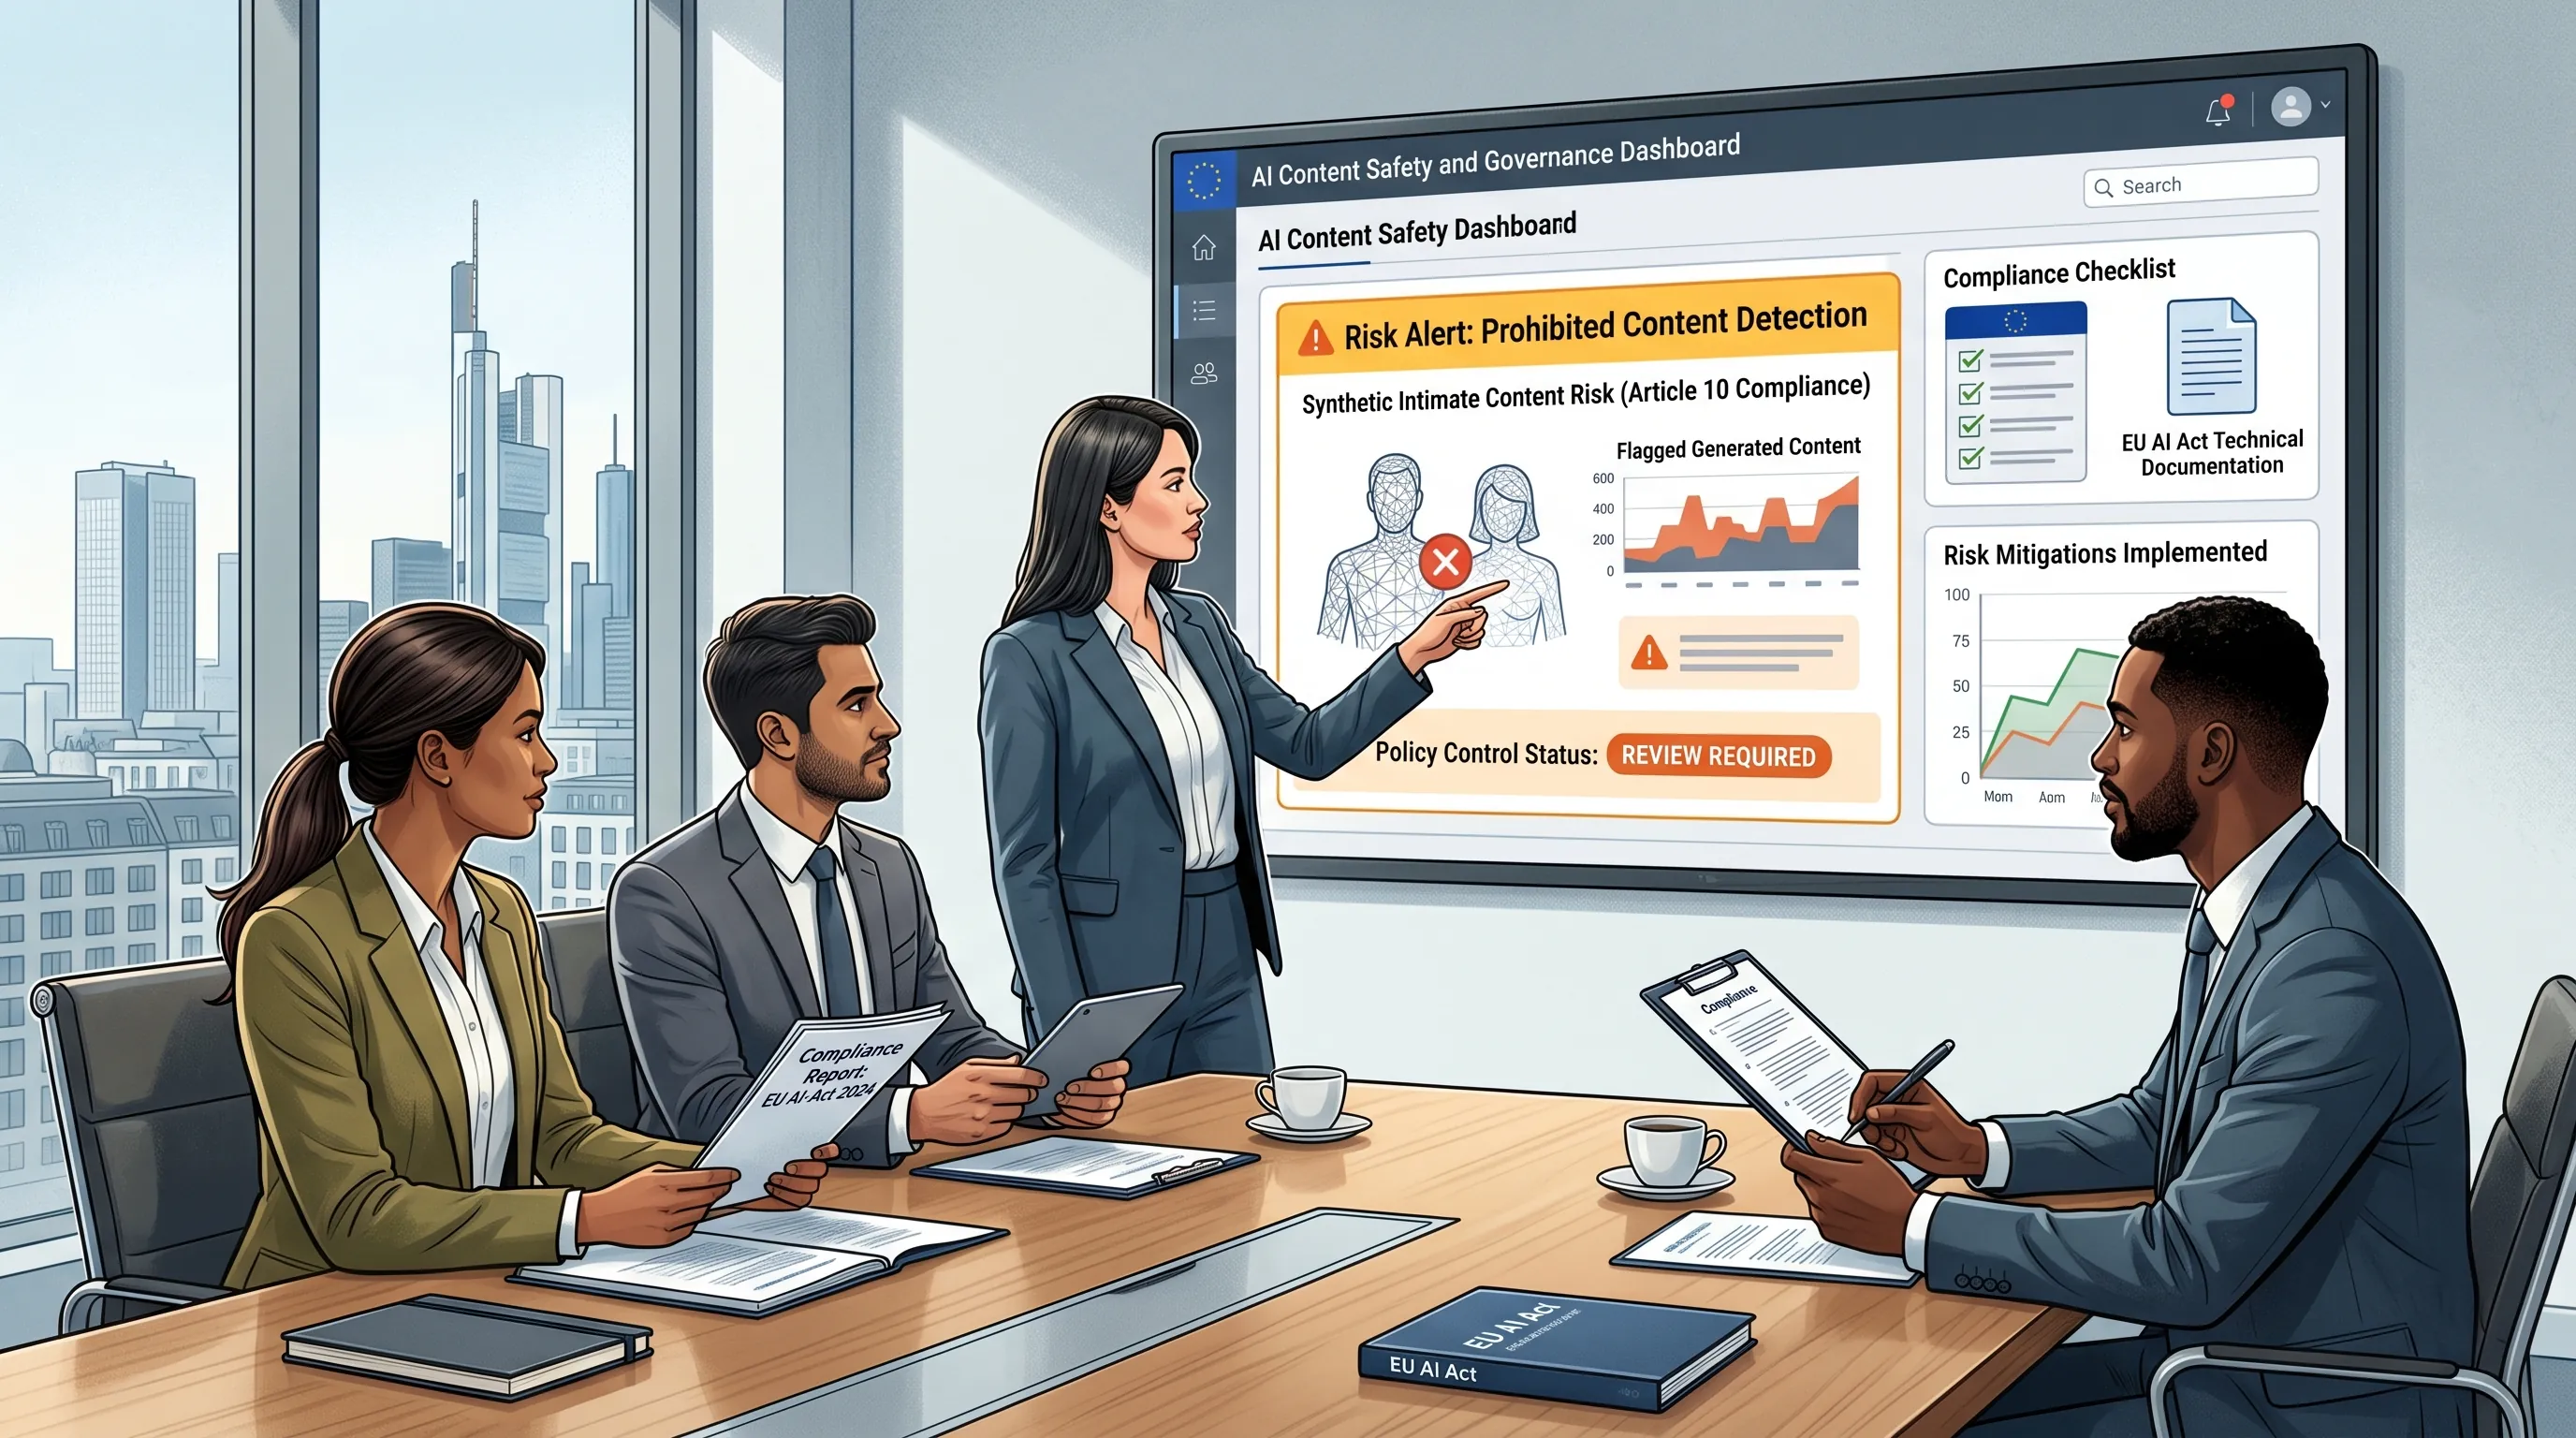
What changed on 7 May 2026
Regulation (EU) 2026/1744 adds prohibitions concerning AI practices involving non-consensual sexual or intimate content and child sexual abuse material. The provisions are in force and apply from 2 December 2026.
That distinction matters: the regulation is in force, while the new Article 5 provisions apply from 2 December 2026. Planning should use the consolidated text without presenting the provisions as already applicable.
What the nudification ban is really about
This is not just a content-labeling issue. It is a prohibited-practices issue. A deployer does not need to operate a consumer "nudification app" to have review work to do.
| Risk bucket | Practical review question |
|---|---|
| Fake intimate image or video generation | Can the system generate or transform content that creates intimate synthetic media of real people without consent? |
| Workflow enablement | Do templates, shortcuts, plugins, or editing tools make prohibited generation materially easier? |
| Child sexual abuse material | Do safety controls specifically block child sexual abuse material and ambiguous age-related abuse patterns? |
| Third-party model exposure | Could imported models, wrappers, extensions, or APIs bypass the organisation's normal controls? |
What deployers should review now
- Use-case mapping: Identify whether internal or customer-facing image, video, avatar, or transformation features could be misused for intimate synthetic content.
- Vendor capability review: Ask providers whether their model, API, or app can generate, transform, or infer nudity or explicit intimate imagery.
- Safety control review: Check whether the provider blocks prompts, uploads, fine-tuning, and editing workflows linked to non-consensual intimate-content generation.
- Abuse reporting path: Confirm how flagged outputs, user complaints, and urgent escalations are handled.
- Acceptable-use controls: Check whether contracts, product terms, and internal policies prohibit these use cases.
- Evidence file: Retain due diligence records, policy updates, approval notes, and test results.
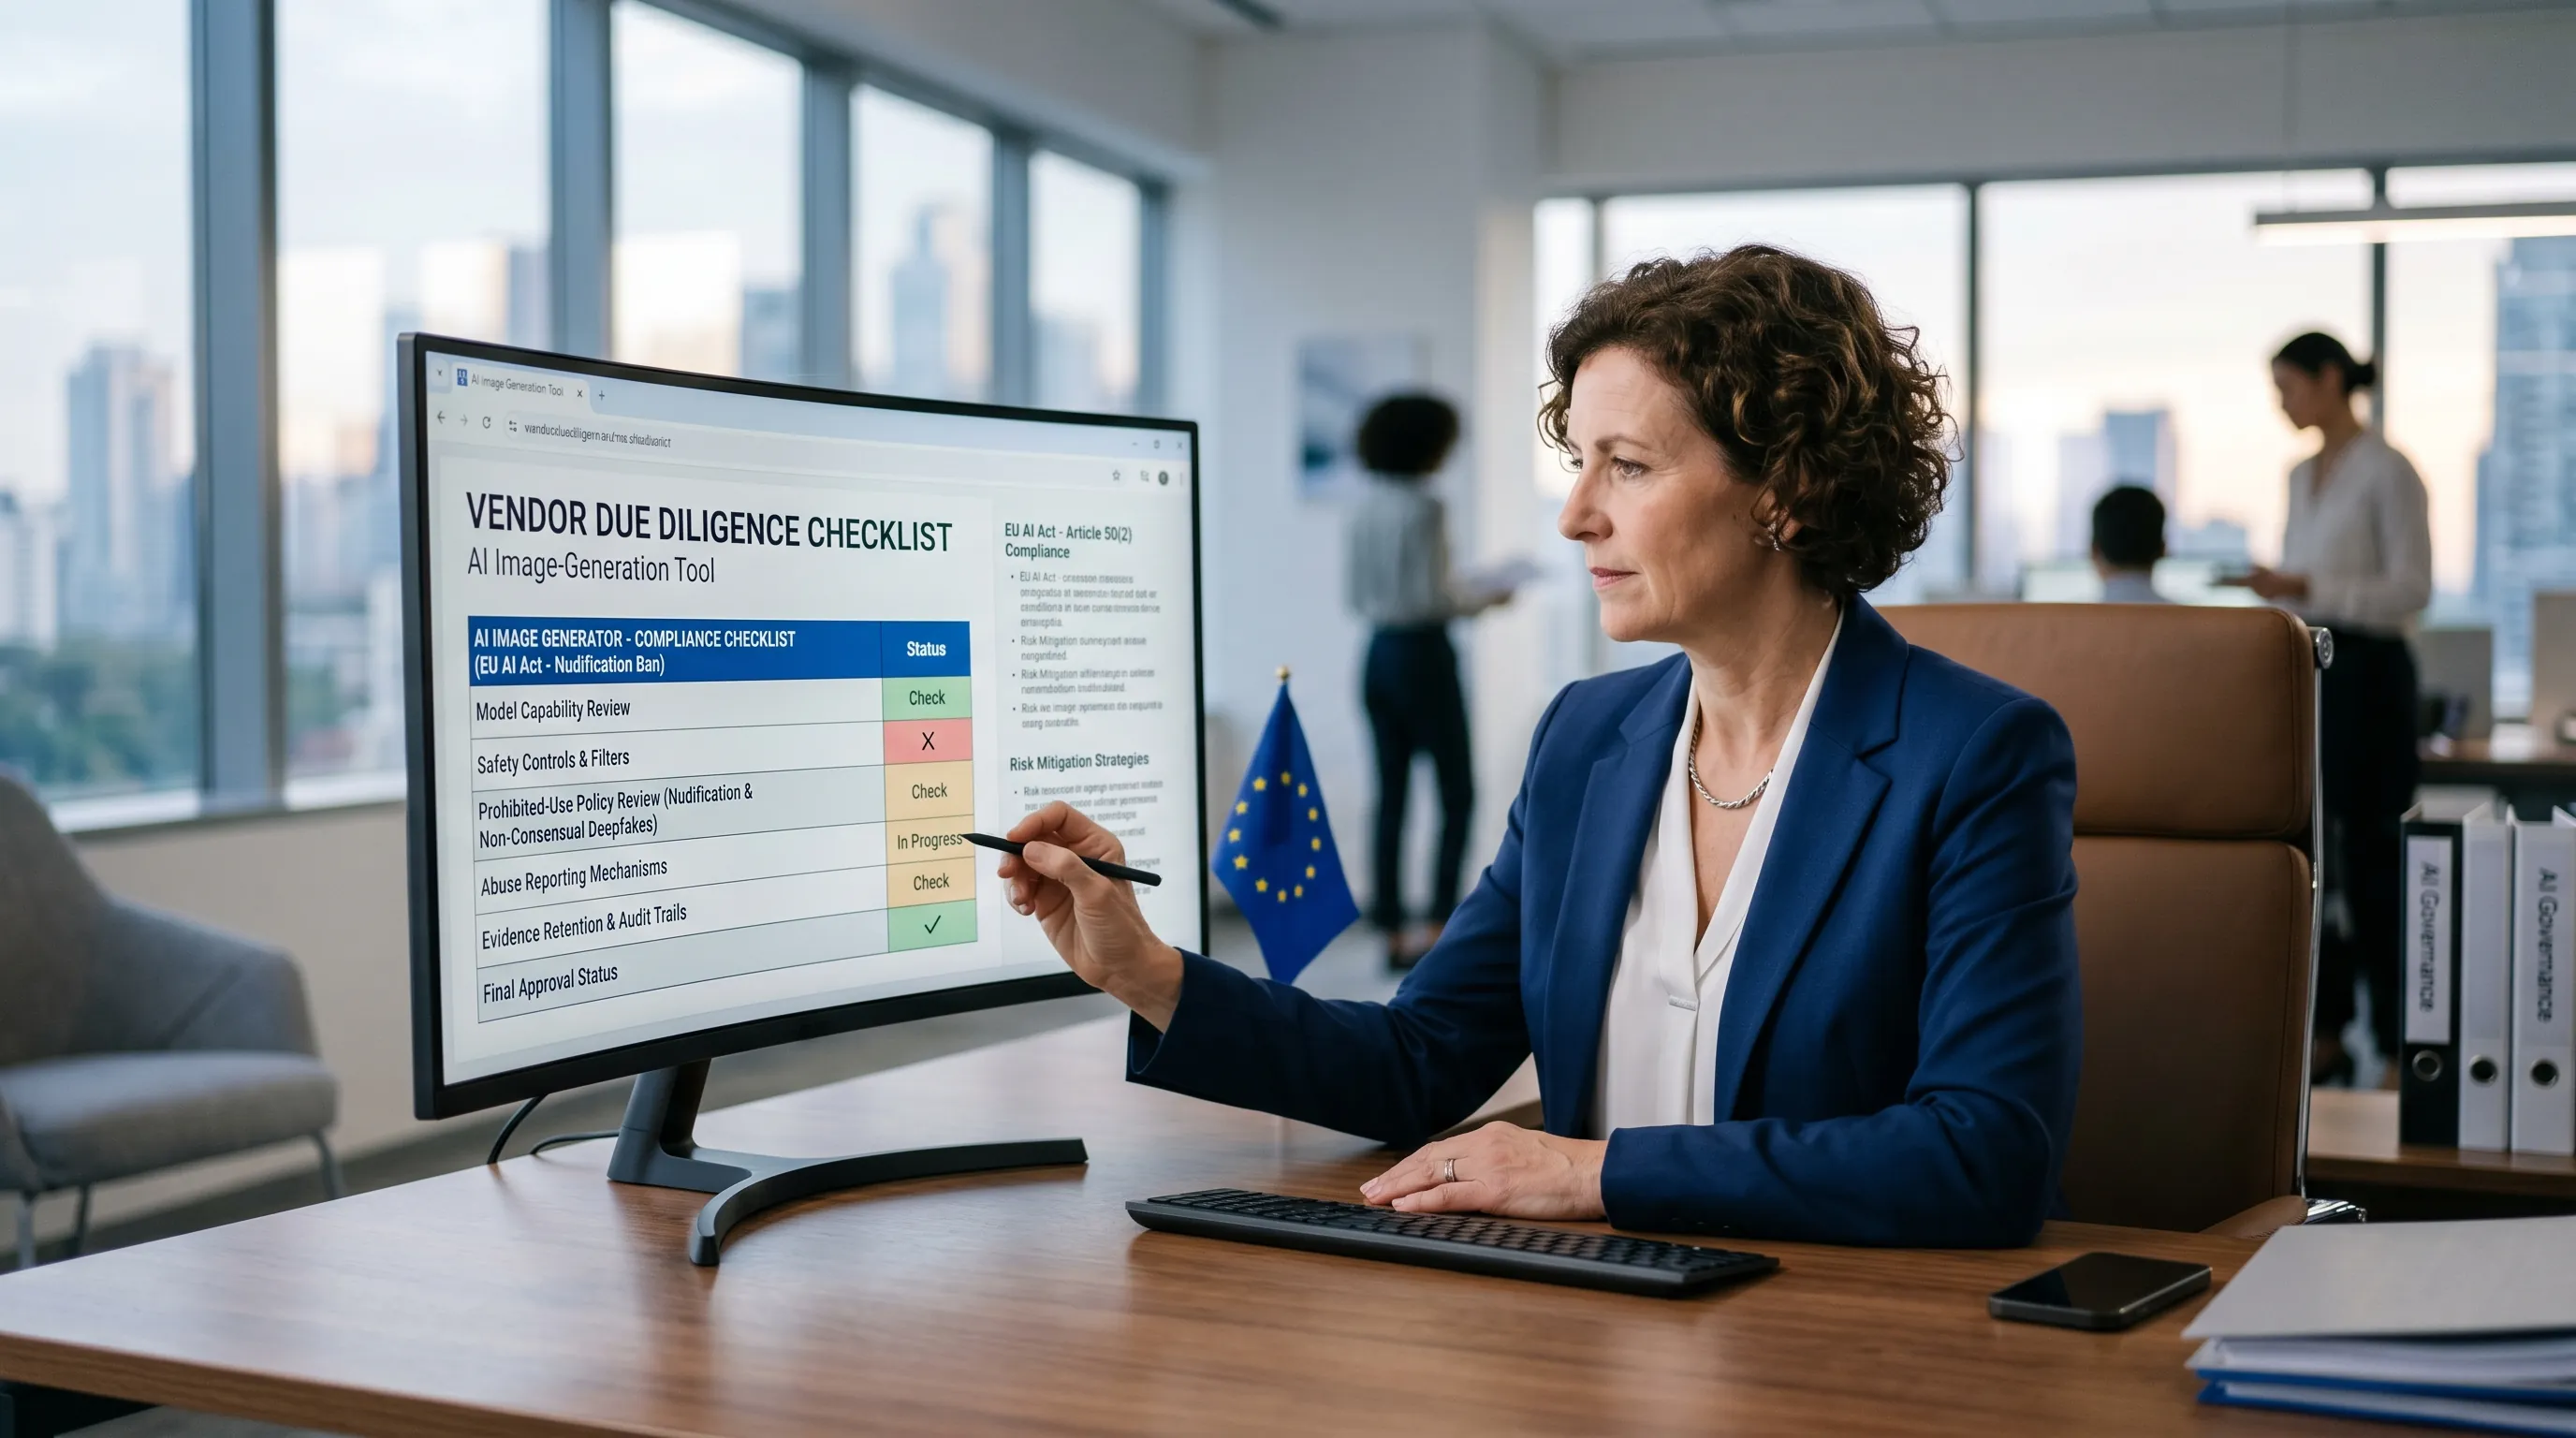
Vendor questions to ask
- Does the system generate or transform image, video, or avatar content in ways that could be used to create intimate synthetic media?
- Are prompts, uploads, and editing functions filtered for non-consensual intimate-content generation?
- Are minors' likenesses, age ambiguity, and sexualised outputs specifically covered by safety controls?
- Does the vendor monitor abuse patterns and retrain or patch safety controls?
- Can the vendor provide test evidence, policy documentation, incident-handling procedures, or model cards?
- Are logs, moderation decisions, and user-reporting events retained in an auditable way?
- Can the system be fine-tuned or extended through third-party plugins that bypass safeguards?
Evidence to retain
| Evidence artifact | Why it matters |
|---|---|
| Feature inventory entry | Shows the system, owner, purpose, users, data categories, and content-generation capability. |
| Vendor questionnaire response | Records what the supplier said about model capability, restrictions, and safety controls. |
| Safety-control summary | Documents prompt filtering, upload checks, moderation, abuse reporting, and escalation routes. |
| Approval or rejection note | Shows whether the feature was approved, restricted, disabled, or escalated for legal review. |
| Regulatory status note | Separates current published-law decisions from Regulation (EU) 2026/1744 provisions and their application dates. |
Common mistakes
The biggest mistake: treating this as a consumer-app issue only. Enterprise teams often use image, avatar, video, design, HR, marketing, and support tools without checking the underlying model capability or plugin path.
- assuming "we are only a deployer" means no review is needed
- reviewing only the front-end feature while ignoring the model and API capability
- accepting marketing claims instead of asking for test evidence
- ignoring plugins, wrappers, fine-tuning, or editing modules
- confusing the regulation's entry into force with the provisions' 2 December 2026 application date
What to do next
If a system touches image generation, transformation, face editing, avatar creation, or visual manipulation, review it now. Update the AI system inventory, run vendor due diligence, confirm prohibited-practice exposure, and keep an evidence trail that records what was checked and when.
FAQ
Direct answers on the Regulation (EU) 2026/1744 provisions, deployer review duties, vendor checks, and evidence retention.
No. Regulation (EU) 2026/1744 is already in force. Its new Article 5(1)(ba) and (bb) provisions and related paragraphs apply from 2 December 2026. Use the consolidated AI Act to check scope, conditions and exceptions.
Regulation (EU) 2026/1744 added Article 5 provisions concerning specified realistic non-consensual sexual or intimate content and child sexual abuse material, subject to statutory conditions and exceptions. Use the consolidated AI Act for the final numbering and text.
Deployers still choose vendors, activate features, approve workflows, and expose users to system outputs. A deployer evidence file should record vendor capability checks, safety controls, acceptable-use restrictions, escalation paths, and the decision note explaining whether a feature was approved, restricted, or rejected.
No. The nudification-ban review is not limited to consumer photo apps. Enterprise image, video, avatar, marketing, HR, customer-support, or design workflows can raise review questions if third-party models, plugins, or editing features could enable intimate synthetic-content generation.
An organisation should keep the use-case review, vendor questionnaire, safety-control summary, approval or rejection note, escalation path, and dated legal-status record. The legal-status record should separate current published-law decisions from Regulation (EU) 2026/1744 provisions and their application dates.